DevSecOps GitHub Actions CI/CD Pack for Docker
A downloadable toolkit
DevSecOps GitHub Actions CI/CD Pack for Docker
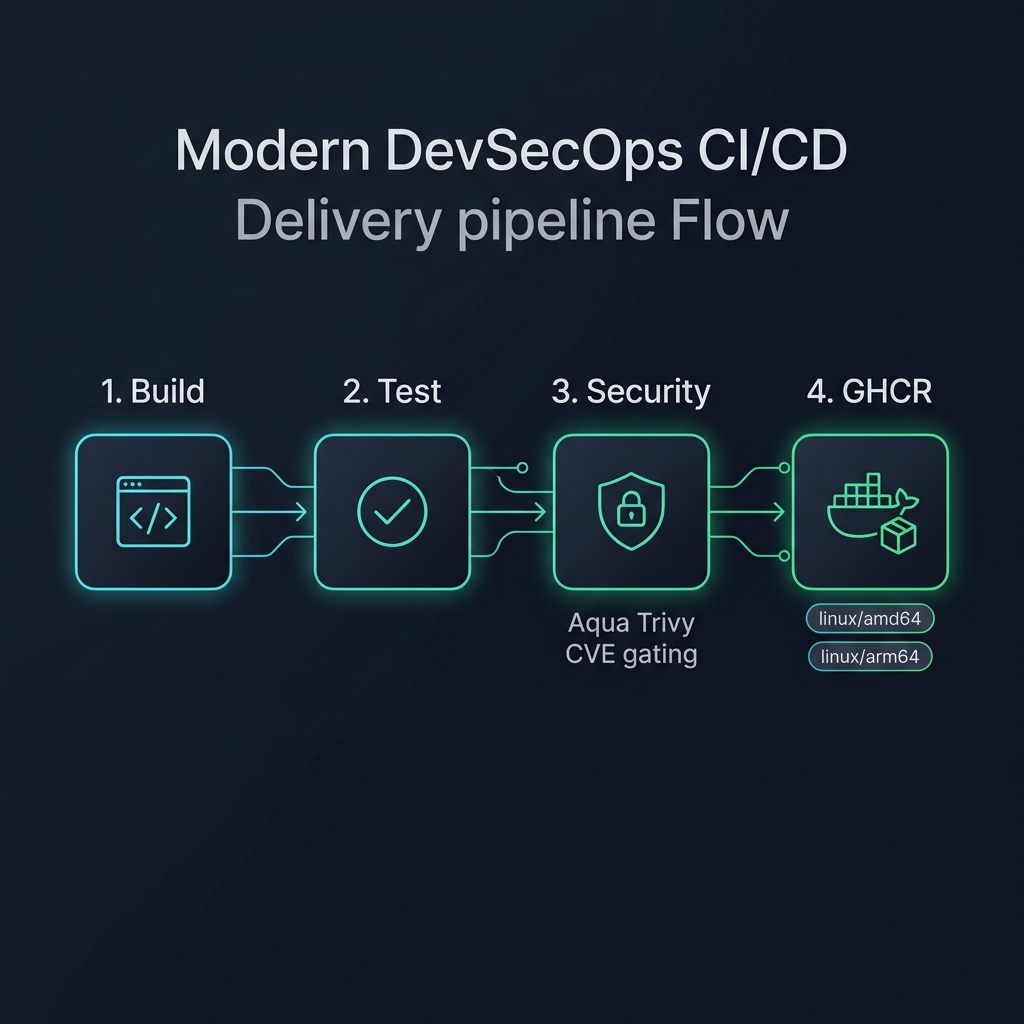
Production-ready DevSecOps CI/CD starter pack with automated vulnerability scanning, multi-architecture Docker builds, SBOM generation, GHCR publishing, and secure GitHub Actions workflows.
Stop rebuilding CI/CD pipelines from scratch.
This pack gives you a ready-to-adapt DevSecOps foundation for Dockerized projects, built around secure GitHub Actions practices, least-privilege permissions, immutable action pins, automated security scanning, and practical Node.js and Python examples.
Use the included workflows and templates as a solid starting point for your own projects, client work, SaaS applications, or internal development environments.
🚀 What's Included
🛡️ Automated Security Scanning with Trivy
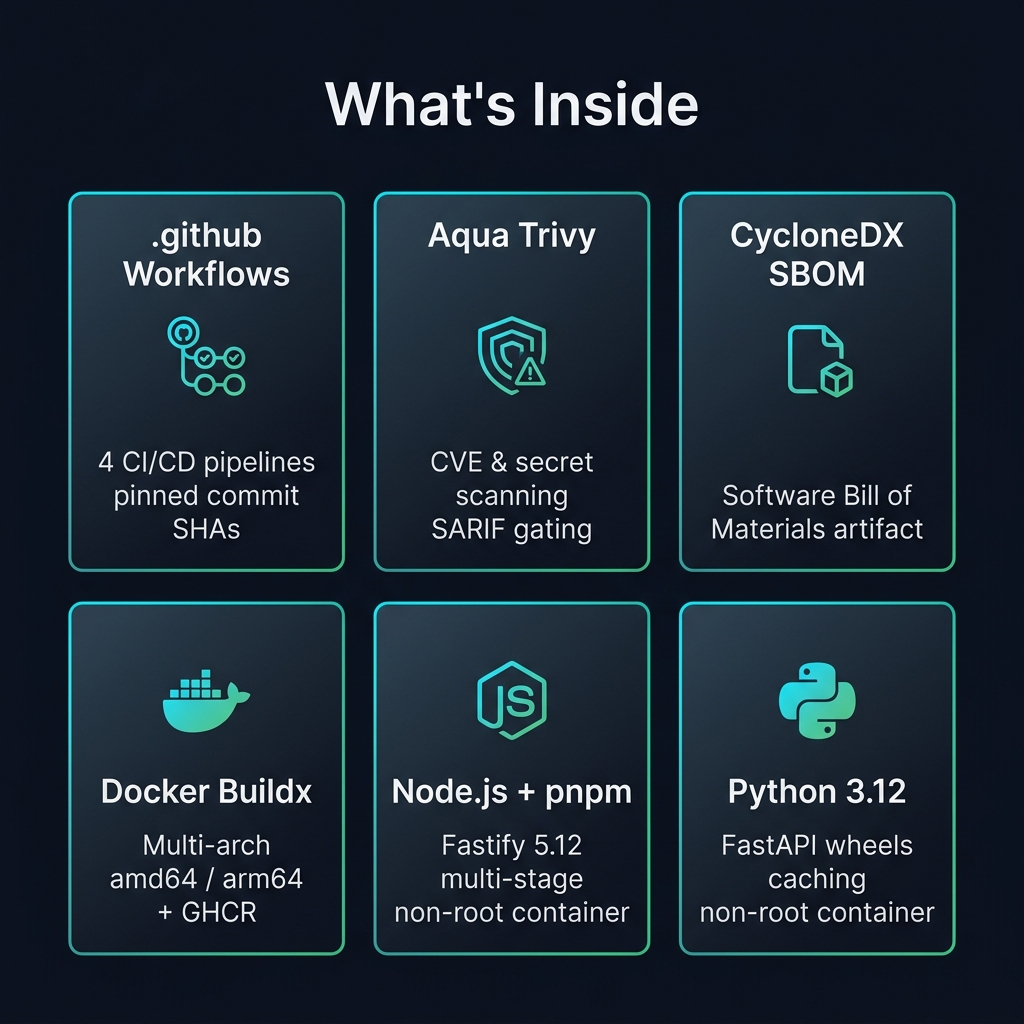
Scan dependencies, filesystem vulnerabilities, exposed secrets, and IaC misconfigurations. SARIF reports can be uploaded directly to GitHub Code Scanning, with a security gate that blocks builds when CRITICAL vulnerabilities are detected.
🐳 Multi-Architecture Docker Builds
Build container images for both linux/amd64 and linux/arm64 using Docker Buildx and GitHub Actions caching.
📦 GitHub Container Registry Publishing
Publish Docker images directly to GHCR using GitHub's built-in GITHUB_TOKEN, with documented permissions and setup instructions.
📜 Automated SBOM Generation
Generate a CycloneDX Software Bill of Materials for your container images and store it as a downloadable GitHub Actions artifact.
🏷️ GitHub Release Workflow
Automatically generate GitHub Releases when version tags such as v1.0.0 are pushed, including generated release notes and container pull instructions.
🤖 Dependabot Configuration
Weekly update checks for:
- GitHub Actions
- Docker dependencies
- Node.js / pnpm dependencies
- Python dependencies
💻 Local Security Tools
Run Trivy locally without installing it directly:
- Bash script for Linux/macOS
- PowerShell script for Windows
🔧 Docker Validation Script
Includes local Dockerfile linting, image build validation, container startup, and healthcheck testing.
📦 Production-Ready Docker Templates
Includes hardened multi-stage Docker examples for:
Node.js
- Fastify
- pnpm
- Node.js 22
- Non-root user
- Healthcheck
- Graceful shutdown
- Multi-stage build
Python
- FastAPI
- Uvicorn
- Python 3.12
- Pre-built dependency wheels
- Non-root user
- Native healthcheck
- Multi-stage build
🔐 Security-Focused GitHub Actions
The included workflows follow practical supply-chain security practices:
- Third-party GitHub Actions pinned to full commit SHAs
- Explicit least-privilege GITHUB_TOKEN permissions
- persist-credentials: false
- Trivy security gating
- SARIF reporting
- Automated SBOM generation
- Dependency update automation
- Safer workflow input handling
✅ Tested & Validated
The pack has been locally validated before release:
- ✔ Node.js Docker image successfully built and executed
- ✔ Python Docker image successfully built and executed
- ✔ /health endpoints verified with HTTP 200 OK
- ✔ GitHub Actions validated with actionlint — 0 errors
- ✔ Workflows audited with zizmor — 0 findings
- ✔ Node.js dependencies checked with pnpm audit — 0 known vulnerabilities
- ✔ Docker containers run as non-root users
- ✔ Third-party Actions pinned to full commit SHAs
📂 Inside the Download
devsecops-github-actions-pack/
├── .github/
│ ├── dependabot.yml
│ └── workflows/
│ ├── ci.yml
│ ├── docker-build.yml
│ ├── security-scan.yml
│ └── release.yml
│
├── templates/
│ ├── Dockerfile.nodejs
│ ├── Dockerfile.python
│ ├── docker-compose.yml
│ ├── .dockerignore
│ └── .env.example
│
├── scripts/
│ ├── local-security-check.sh
│ ├── local-security-check.ps1
│ └── validate-docker.sh
│
├── examples/
│ ├── node/
│ └── python/
│
├── docs/
│ ├── QUICKSTART.md
│ ├── GHCR_SETUP.md
│ ├── SECRETS.md
│ └── TROUBLESHOOTING.md
│
├── LICENSE.txt
└── README.md
⚡ Quick Start
Copy the workflows and templates into your Dockerized GitHub repository, review the included configuration, adjust the Dockerfile and paths for your application, and push your changes.
A detailed Quick Start guide, GHCR setup guide, secrets reference, and troubleshooting documentation are included.
👨💻 Who Is This For?
Ideal for:
- DevOps Engineers
- DevSecOps Engineers
- Backend Developers
- Platform Engineers
- SREs
- Freelancers
- SaaS developers
- Students building production-style portfolios
- Teams standardizing GitHub Actions pipelines
📄 License
Commercial use is permitted in your own projects, SaaS applications, internal company repositories, and client projects.
Redistribution, resale, sublicensing, republishing, or repackaging this toolkit as a competing template or downloadable product is not permitted.
📥 Digital Product
This is a digital ZIP download containing source code, GitHub Actions workflows, Docker templates, scripts, examples, and documentation.
No physical product will be shipped.
Version: 1.0.0
You will get a ZIP (32KB) file
Purchase
In order to download this toolkit you must purchase it at or above the minimum price of $12.99 USD. You will get access to the following files: